Building a HIPAA compliant dedicated server environment needs a strict division of physical, technical, and administrative safeguards. By securing the physical layer through a certified US datacenter, engineering teams can configure their own OS-level encryption, firewalls, and audit logging. This grants complete hardware isolation, while minimising egress fees for massive medical workloads, and keeps you compliant under a clear shared responsibility model.
Over the past decade, our infrastructure architects have helped several telehealth startups, genomic research labs, and hospital IT directors transition away from overpriced HIPAA managed hosting environments. We see a recurring problem in the medical tech industry: engineering teams bleed capital by deploying sensitive ePHI (Electronic Protected Health Information) on shared public clouds or heavily marked-up managed compliance hosts, which often charge over $1000 dollars for a simple dedicated server machine.
HIPAA compliance operates on a strict shared responsibility model. Many niche hosting providers package their offerings as fully managed HIPAA compliant servers, bundling third-party host intrusion detection (HIDS), endpoint monitoring, and automated vulnerability scans. They often charge triple the standard hardware rate for these software layers. For medical SaaS providers with capable in-house sysadmins or DevOps engineers, this managed layer is an unnecessary payout. Your team already knows how to harden a Linux kernel and deploy centralized audit logging. You just need the right physical foundation.
The scope of ePHI regulations
A common misconception among international medical tech startups is that US healthcare regulations only matter if your corporate headquarters is physically located in the United States. In reality, the jurisdiction is determined entirely by the data itself.
Whether your development team is based in Silicon Valley, London, or Berlin, if your platform processes, stores, or transmits the ePHI of US citizens, you fall under the jurisdiction of the Department of Health and Human Services (HHS). Failure to implement proper safeguards exposes your business to severe financial penalties and blocks you from selling software to US healthcare providers. The infrastructure housing that data requires verifiable, documented security protocols regardless of your company's origin.
Fulfilling physical safeguards
Under 45 CFR § 164.310, the HIPAA Security Rule mandates strict physical safeguards to limit facility access to authorized personnel. You simply cannot pass a compliance audit if your servers sit in an uncertified facility. The physical location must be highly restricted and constantly monitored.
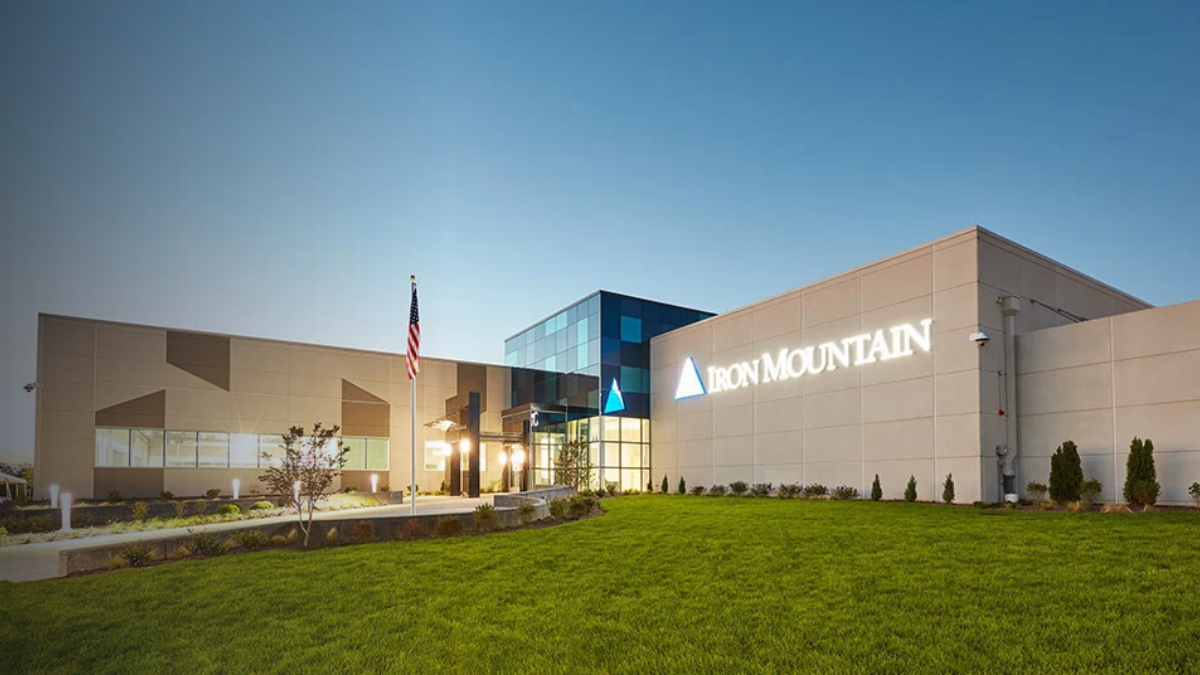
We rack our enterprise hardware directly inside the Iron Mountain data center in Edison, New Jersey. This Tier III facility holds ISO 27001, SOC 2 Type II, and FISMA High certifications. It operates with biometric access controls, mantrap doors, 24/7 armed monitoring, and strict physical audit trails. By deploying your hardware here, you are able to satisfy the physical access requirements of your compliance audit. We supply these facility audit reports directly to your compliance officers.
The HIPAA business associate agreement
Under US federal law, covered entities must execute a Business Associate Agreement (BAA) with vendors that store or process ePHI. However, the application of this rule depends on how you architect your encryption boundary.
If your platform encrypts all data end-to-end prior to storage, and you retain exclusive control of the decryption keys, federal HHS guidance often classifies the infrastructure provider as a mere conduit or hardware supplier. In this scenario, we cannot access the ePHI, and a BAA with your infrastructure provider is not strictly required. However, if you do not encrypt your transit data, then your infrastructure provider is classified as a business associate, and is required to sign the BAA with you.
On the other hand, if your hospital clients or corporate legal team strictly mandate a signed agreement for their compliance documentation, our legal team will evaluate the request. We routinely sign limited-scope IaaS BAAs that bind our liability strictly to physical hardware maintenance and facility security.
No multi-tenant risk
Public cloud environments operate on shared hypervisors. When you deploy a cloud VM, your encrypted patient database might sit on the exact same physical CPU and RAM module as an unknown third-party tenant. Cross-tenant attacks, cache side-channel vulnerabilities, and hypervisor exploits present an unacceptable risk profile for highly sensitive medical data.
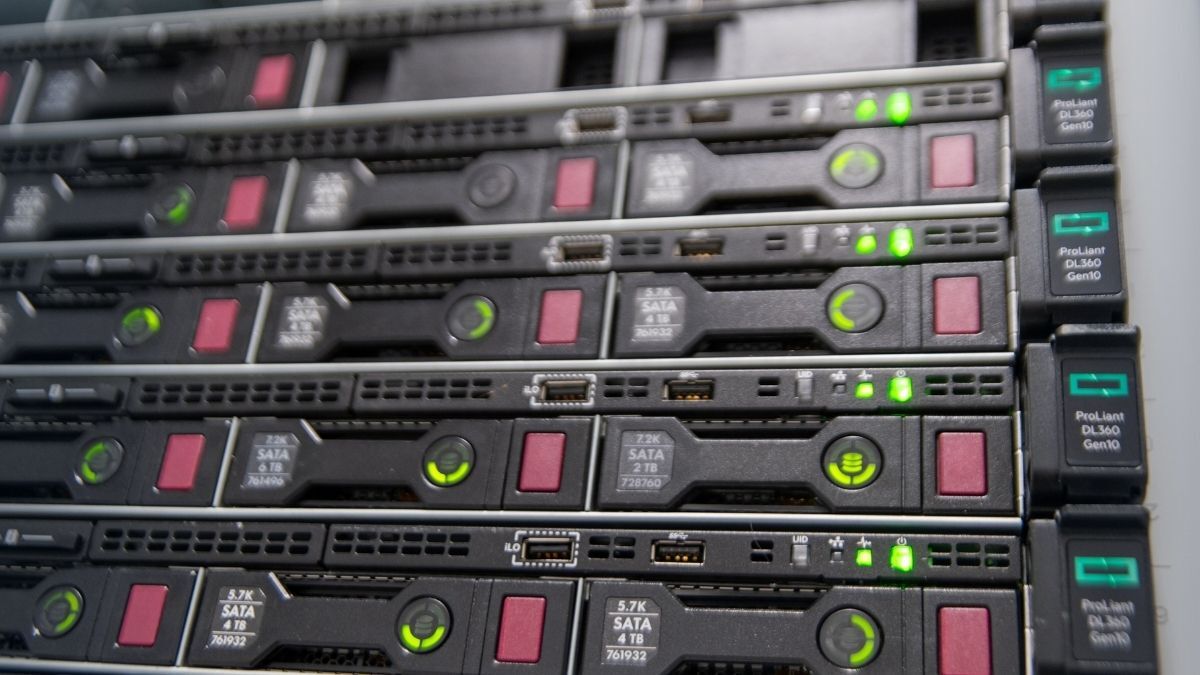
A HIPAA dedicated server provides absolute single-tenant isolation. With our HPE and Supermicro chassis, no external tenants share your physical bus, CPU cache, or storage controllers. You achieve true hardware sovereignty. And for bandwidth, your bare metal servers also get dedicated bandwidth ports. This isolation ensures predictable compute performance for intensive diagnostic AI models and completely eliminates the security risks inherent to multi-tenant public cloud scaling.
Handling medical imaging and genomics
Medical workloads are notoriously data-intensive. Genomic sequencing pipelines, PACS (Picture Archiving and Communication System) medical imaging, and high-definition telehealth video streams push terabytes of data daily. Public cloud providers penalize this traffic heavily, charging roughly $0.09 per GB for data egress. We regularly analyze cloud bills for telehealth startups where the AWS egress fees far exceed their actual compute costs.
Our network infrastructure help you avoid these financial bottlenecks. We operate an 19+ Tbps global network backbone. Every dedicated server includes 25TB of free transit on a 2Gbps uplink by default. For massive healthcare data lakes, we offer unmetered ports scaling from 1Gbps up to 50Gbps with very affordable bandwidth costs. If your application logic must remain in a specific cloud environment, you can slash your egress costs by pushing traffic through our Cloud Connect service directly into our bare metal storage nodes.
Transit encryption and isolated networking
Healthcare regulations ask for strict network separation between public-facing web servers and backend patient databases. Exposing an ePHI database node to the public internet, even momentarily, is a critical compliance violation.
We provide isolated private networking free of charge. Our network engineers routinely provision private Layer-2 VLANs that connect front-end processing nodes directly to back-end storage clusters. This keeps internal hospital API traffic and database queries completely off public transit routes. Your HIPAA compliant dedicated server remains securely air-gapped from external threats while communicating at full port speed internally.
Bare metal is your HIPAA foundation
On contrary to HIPAA managed hosting providers, we offer you the dedicated servers with absolute root control. We do not sell software firewalls, we do not patch your operating systems, and we do not manage your endpoint security. Our engineers never touch your data layer.
What we do is provide a vastly superior, budget-friendly foundation for you to build your own HIPAA compliant server hosting environment. By deploying directly with NovoServe LLC—an independent, registered US entity—you keep your data strictly within US legal jurisdiction inside a US-owned datacenter. Our US entity is strictly seaprate from our European operation – NovoServe B.V. You get enterprise-grade HPE hardware, full root IPMI access, and 50Gbps unmetered bandwidth capabilities. You skip the managed service markups entirely and empower your DevOps team to configure custom LUKS encryption and audit logging precisely how your compliance framework dictates.